

Aspiring SOC Analyst · Cybersecurity Practitioner · Blue Team


Observe → Investigate → Detect → Validate → Document


About · Projects · Evidence · Skills · Credentials · Goals · Connect
I'm a cybersecurity practitioner from Multan, Pakistan, working toward my first SOC Analyst / Cybersecurity Analyst role. I completed an EduQual Level 3 Diploma in Cloud Cyber Security with 91% and earned the Cybrixen Certified SOC Analyst (CCSA) certification.
My interest is in understanding what happened behind an alert: which account was involved, what process ran, how the activity developed, and what evidence supports the next response step. My projects cover Windows endpoint monitoring, Splunk detections, malware behavior analysis, AWS log investigations, and automated containment.
Splunk is my primary SIEM. I also have project experience with Wazuh, Sysmon, Sigma, Chainsaw, Wireshark, AWS CloudTrail, Amazon Athena, and Shuffle.
I share my work through investigation reports, detection queries, screenshots, and troubleshooting notes so others can follow the reasoning and reproduce the labs.
Build → Observe → Investigate → Detect → Validate → Document
📊 Portfolio snapshot — expand to see my areas of practical work
| Area | What I've built or investigated |
|---|---|
| SOC monitoring | Windows log collection, RDP brute-force detection, SPL searches, and Splunk dashboards |
| Detection engineering | Sigma rules validated against Sysmon logs, command-line hunting, and MITRE ATT&CK mapping |
| Cloud security | CloudTrail → S3 → Athena logging and SQL investigation of simulated IAM compromise |
| Security automation | Shuffle playbook connecting IP enrichment, conditional EC2 isolation, and Slack notification |
| Network investigations | Emotet traffic analysis, C2 identification, IOC extraction, and Windows attack investigations |
| Security tooling | Python web scanner with a CLI, Flask interface, and Markdown/PDF reporting |
| Industrial security | MQTT authentication and TLS, Node-RED monitoring, and Wazuh alerts in an Industry 4.0 demo |
|
Turned sandbox observations into persistence and C2 Sigma rules, validated using controlled reproductions.
Evidence: Two rules matched real endpoint telemetry. |
Built cloud logging and investigated a simulated IAM compromise using raw CloudTrail evidence.
Evidence: Six key events reconstructed from 356 logged actions. |
|
Connected IP reputation enrichment to conditional quarantine of a lab EC2 instance and analyst notification.
Evidence: Low-score skip and high-score isolation paths verified. |
Built Windows log forwarding, SPL detections, and a dashboard for RDP brute-force investigation.
Evidence: 15 failed logons followed by one successful authentication. |
| Project | What I did | Main tools |
|---|---|---|
| AD Kerberoasting Detection | Built an AWS-hosted Samba AD lab, simulated Kerberoasting, investigated RC4 service-ticket requests in Samba logs, and documented response actions and a Sigma detection rule | Samba AD, Impacket, Kerberos tools, John the Ripper, Sigma |
| FortifyWebX Scanner | Built a crawler with five passive checks, severity scoring, CLI/web interfaces, and Markdown/PDF reports; tested with Juice Shop and DVWA | Python, Flask, Requests, BeautifulSoup, Docker |
| SOC Investigations | Investigated Emotet PCAP traffic, RDP brute-force activity, and Windows attack simulations; extracted IOCs and wrote investigation reports | Wireshark, VirusTotal, Event Viewer, Hydra |
| Industry 4.0 Security | Implemented MQTT authentication and TLS, built a sensor dashboard, and demonstrated Wazuh brute-force alerts with IEC 62443/NIST CSF mappings | Mosquitto, OpenSSL, Node-RED, Wazuh, Ubuntu |
| Networking Notes | Documented networking fundamentals, protocols, subnetting, monitoring, and their relevance to SOC investigations | OSI/TCP-IP, DNS, DHCP, VLANs, VPNs, IDS/IPS |
🦠 Agent Tesla — analysis, validation, and scope
- Analyzed an existing ANY.RUN public sandbox report to identify Agent Tesla scheduled-task persistence and SMTP-based C2 behavior.
- Extracted indicators and mapped findings to T1053.005 and T1071.003.
- Wrote two Sigma rules: a behavior-based persistence rule and an indicator-based C2 rule.
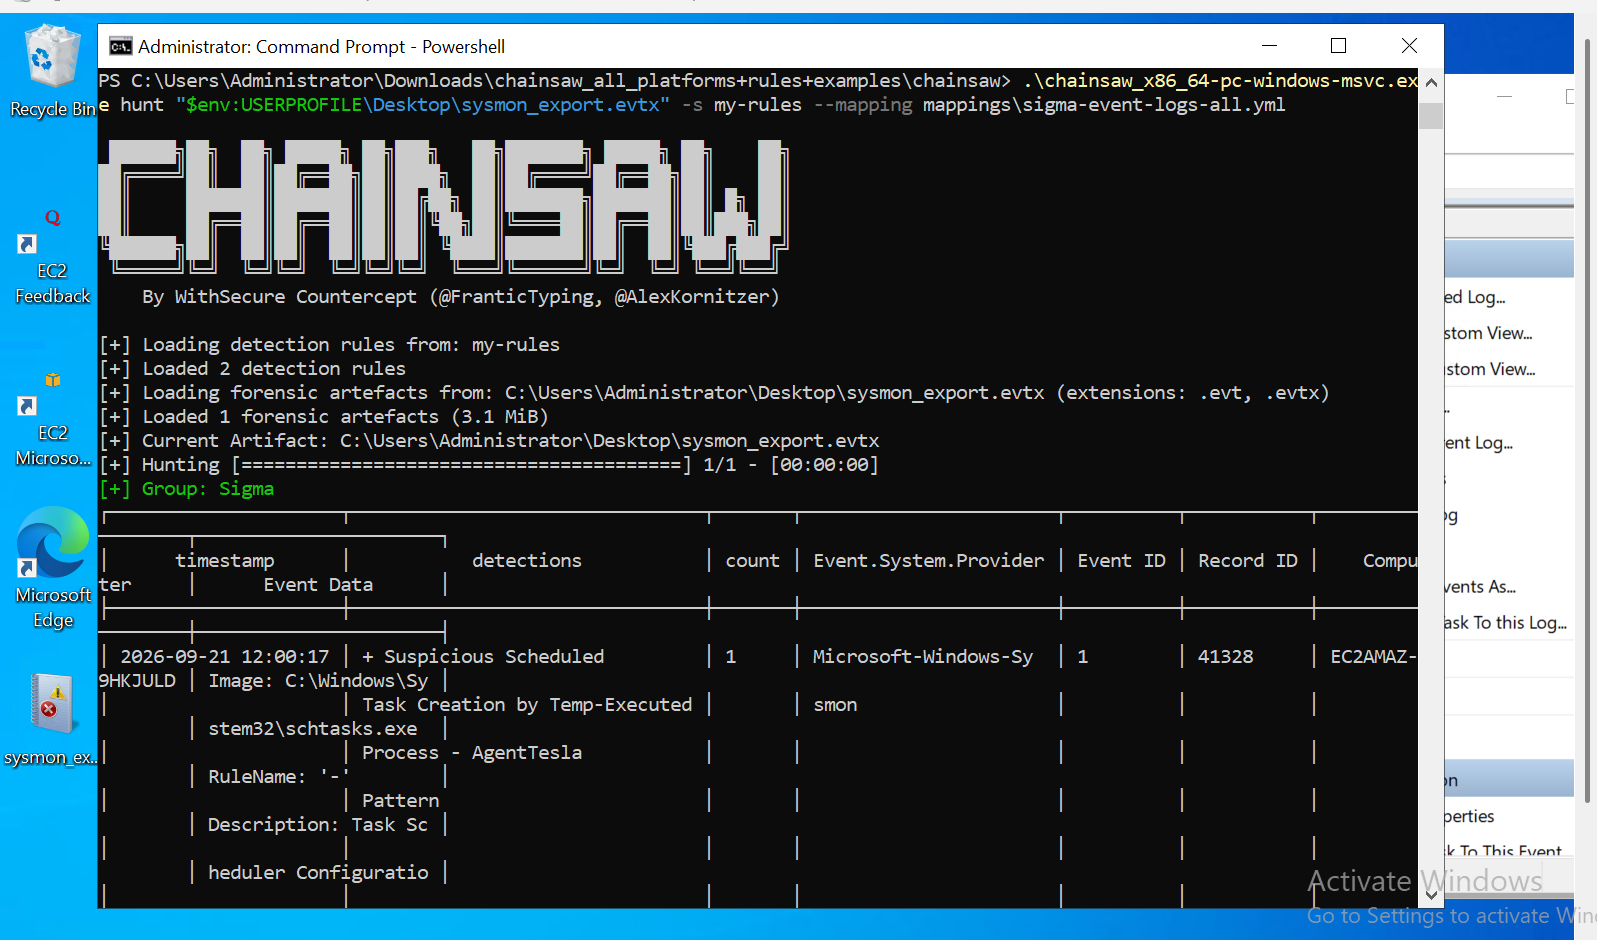
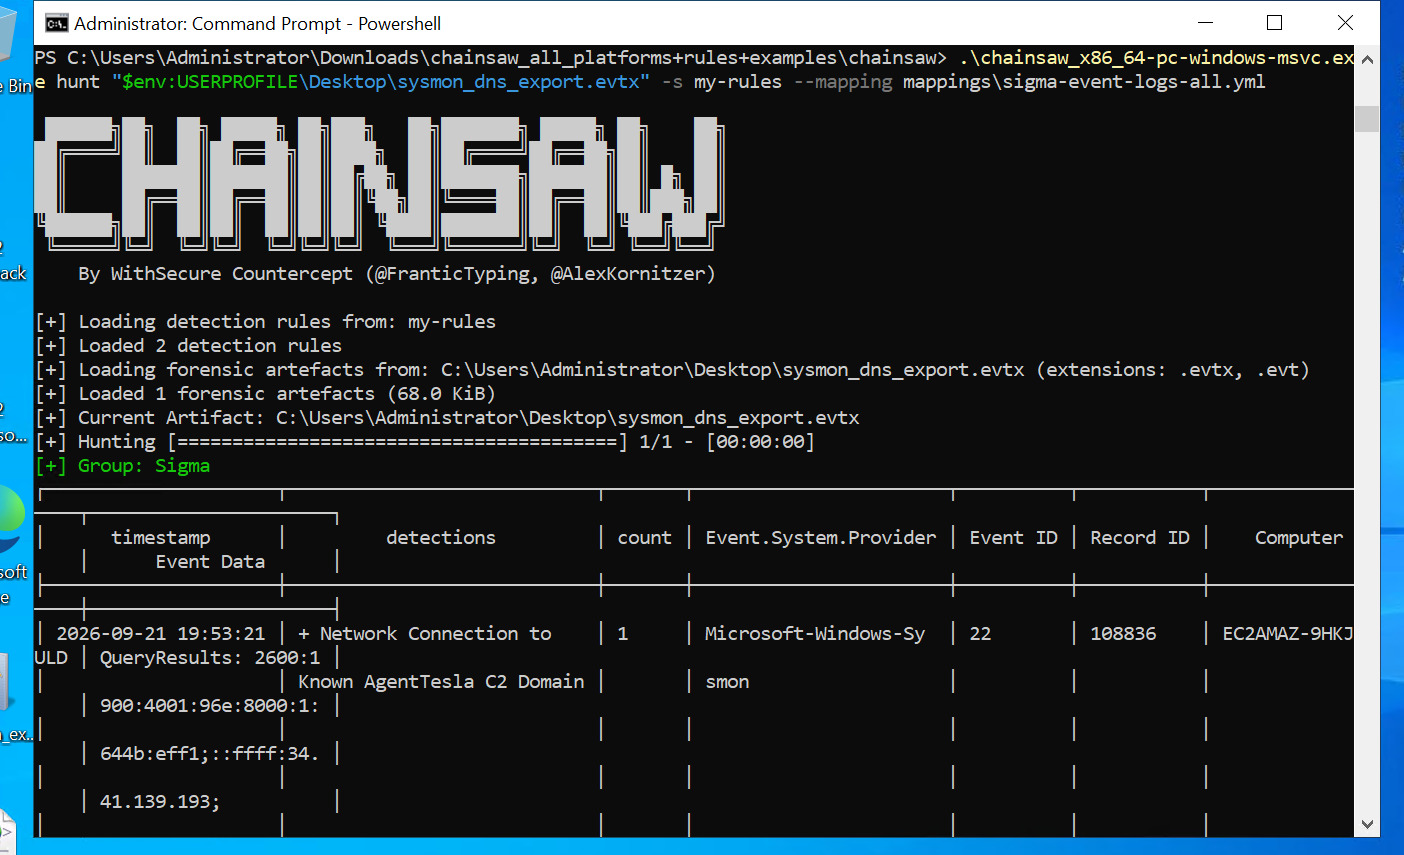
- Reproduced the persistence pattern and a DNS lookup on an AWS Windows host, then confirmed both rules matched real Sysmon logs using Chainsaw.
Scope: validation used controlled behavior reproduction; the malware binary was not executed on the AWS host. The rules remain experimental.
☁️ AWS compromise — evidence and behavioral detections
- Built a CloudTrail → S3 → Amazon Athena pipeline.
- Simulated compromised credentials, a login without MFA, IAM privilege escalation, and an unauthorized EC2 launch in my own lab account.
- Investigated the raw logs with SQL and reconstructed six key events from 356 logged actions.
- Added behavioral queries for self-escalation and baseline deviation, including review of legitimate activity flagged as anomalous.
⚙️ SOAR playbook — tested branches and lab boundaries
- Built a Shuffle → AbuseIPDB → AWS Lambda → EC2 quarantine → Slack workflow.
- Used an abuse-confidence threshold greater than 80 to trigger a security-group change on the lab instance.
- Verified both branches: low-score input skipped isolation; high-score input triggered isolation and notification.
- Documented troubleshooting and the authentication, IAM, and asset-mapping changes needed before production use.
🔎 Splunk labs — RDP correlation and command-line hunting
RDP Brute-Force Detection · LotL Command-Line Hunting
- Built a Windows-to-Splunk log pipeline using Sysmon and Splunk Universal Forwarder.
- Investigated 15 failed RDP logons followed by one successful authentication, using Windows events 4625 and 4624.
- Created SPL searches and a dashboard to show failed attempts and the subsequent successful logon.
- Captured the
vssadmin.exe delete shadowscommand pattern with Sysmon Event ID 1, examined process context, and validated an SPL hunt against the ingested evidence.
🖼️ View Agent Tesla detection evidence
Persistence rule: Chainsaw match for the controlled scheduled-task reproduction.
C2 indicator rule: Chainsaw match for a DNS lookup of the analyzed indicator.
🧭 View the SOAR playbook decision flow
This diagram represents the individual IP threat isolation lab.
flowchart TD
    A["Suspicious IP alert"] --> B["AbuseIPDB enrichment"]
    B --> C{"Score greater than 80?"}
    C -->|Yes| D["Lambda: quarantine lab EC2"]
    C -->|No| E["Skip isolation"]
    D --> F["Slack notification"]
SIEM & Detection


Cloud & Automation


Investigation & Development


📋 Expand the skills and practical experience matrix
| Domain | Tools and practical experience |
|---|---|
| SIEM & log analysis | Splunk Enterprise, SPL, Universal Forwarder, dashboards, Windows Event Logs; Wazuh project experience |
| Endpoint detection | Sysmon, Event Viewer, Sigma, Chainsaw, process lineage and command-line analysis |
| Threat intelligence | ANY.RUN report analysis, VirusTotal, AbuseIPDB, IOC extraction and MITRE ATT&CK mapping |
| Cloud security | AWS EC2, IAM, security groups, CloudTrail, S3, Athena SQL and Lambda |
| Automation & scripting | Shuffle workflows, API integration, Python, boto3, Flask; Bash fundamentals |
| Networking & systems | Wireshark, TCP/IP, DNS, Linux/Ubuntu, Windows Server, VirtualBox and Docker |
| Security testing | Nmap, Hydra, Impacket, DVWA and OWASP Juice Shop in authorized labs |
| Reporting | Incident timelines, detection documentation, screenshots, troubleshooting and remediation recommendations |


| Qualification | Achievement |
|---|---|
| EduQual Level 3 Diploma in Cloud Cyber Security | Completed with 91% |
| Cybrixen Certified SOC Analyst (CCSA) | Practical SIEM/EDR assessment: investigations, alert correlation, timelines, true/false positives, and escalation |
FortifyWebX — Cybersecurity Internship · July–September 2026
Completed practical assignments involving reconnaissance, vulnerability assessment, Linux/Windows security testing, web application testing, scanner development, and technical reporting.
Cybrixen — Ambassador
Refer interested learners to Cybrixen and share cybersecurity learning opportunities through professional outreach.
Pakistan Network Solutions (PakNS) — Freelance Business Development Specialist
Support outreach for cybersecurity consultancy and PECB professional training. This role is helping me develop communication skills and understand organizational security and training needs.
My immediate goal is to join a team as an entry-level SOC Analyst or Cybersecurity Analyst, where I can contribute to monitoring, investigation, and clear incident documentation while learning from experienced analysts. I'm open to remote opportunities that accept candidates based in Pakistan.
My next steps are to:
- Deepen my Splunk skills in alert correlation, detection tuning, and false-positive analysis.
- Expand investigations across endpoint, network, and cloud evidence.
- Improve Python/Bash scripting and Linux administration.
- Strengthen automation with authentication, least-privilege access, reliable asset mapping, and analyst approval where appropriate.
- Explore AI-assisted SOC workflows for enrichment and investigation summaries while keeping decisions grounded in evidence.
Longer term, I plan to pursue a BS in Computer Science and grow into detection engineering and cloud security. I want to build useful security tools and detections that help analysts understand threats and respond with confidence.
🗓️ Explore recent project updates and contributions
| Project | Latest repository commit |
|---|---|
| Agent Tesla detection lab |  |
| Cloud log auditing |  |
| IP isolation playbook |  |
View my contribution calendar on GitHub · Browse all repositories
I'm interested in blue-team collaboration, detection engineering, cloud investigations, and entry-level security opportunities.
Based in Pakistan · Open to remote opportunities accepting candidates in Pakistan
Build the environment. Follow the evidence. Validate the detection. Share the learning.